How To Protect Your Business From Digital Identity Fraud


Updated September 4, 2026
Digital identity fraud is a structural risk embedded in every digital channel your business operates. It is more complex than individual identity theft, the payoffs for criminals are larger, and the attack surface keeps expanding as more workflows move online. Every new digital channel you open, whether online payments, remote account access, or digital onboarding, creates another entry point for fraud. PwC's Global Economic Crime and Fraud Survey found that 46% of businesses reported experiencing fraud or digital identity theft in the previous 24 months. Because business identity theft carries larger payoffs than targeting individuals, it is a growing priority for sophisticated fraud rings.
The threat is real. So are the controls. Businesses now have layered, high-assurance tools to stop digital identity fraud before it reaches critical workflows.
Key takeaways
- 46% of businesses reported fraud or digital identity theft in the previous 24 months, according to PwC's Global Economic Crime and Fraud Survey, and one in five large organizations has reported a single fraud incident costing more than $50 million.
- Business identity theft targets the entity directly through EIN fraud, fraudulent UCC filings, and fake tax filings, giving attackers longer detection windows and larger dollar amounts than individual fraud.
- Effective protection requires layered defenses: multi-factor authentication (MFA), strong credential policies, identity verification at every transaction touchpoint, and active monitoring of business credit.
- Attackers cycle through tactics including phishing, credential stuffing, synthetic identity creation, and social engineering until something works. Knowing each method is the first step to closing the gap.
- When a breach occurs, speed determines the blast radius. Knowing your response steps before an incident happens is as important as prevention.
- Platforms like Proof give businesses cryptographically secured audit trails tied to verified identities, producing defensible records at every point where identity, documents, and authorization intersect.
What is digital identity fraud?
Digital identity fraud is the illegal use of stolen personal data or a fabricated persona to commit theft, open unauthorized credit lines, file false returns, or impersonate your business entirely. It is a process: a threat actor finds a weakness, extracts sensitive information, and weaponizes it.
For individuals, that means stolen Social Security numbers, credit card numbers, PINs, or dates of birth. These data points make up a digital identity. Criminals use this information to open new lines of credit, apply for loans, and access other services.
Digital identity fraud also targets businesses directly. The Department of Justice's Office for Victims of Crime defines business identity theft as identity theft committed with the intent to defraud or hurt a business, including financial fraud, tax fraud, and extortion. A bad actor may use your company's EIN, credit profile, or registered identity to open accounts, file fraudulent returns, or damage your brand.
Attackers weaponize business identity through several specific mechanisms:
- Fraudulent business tax returns to exploit refundable tax credits
- Fake W-2s with fictitious withholding used to seed multiple individual returns
- Fraudulent UCC filings that create phantom liens on business assets
Businesses are higher-value targets than individuals because the dollar amounts are larger and detection windows are longer. Offline identity theft had its limits: a stolen wallet, a dumpster dive, a bad actor posing as a vendor. Online fraud has no such ceiling. One compromised credential can open doors to an entire organization's financial and operational records.
What are the warning signs of digital identity fraud?
The warning signs are recognizable if you know what to look for. Watch for these signals:
- Unexpected bills from providers your business never engaged
- Rogue accounts opened in your company's name
- An IRS notice tied to a return you never filed
- Unauthorized transactions on business accounts
- Complaints from vendors or customers about communications or orders they did not initiate
- Unauthorized changes to your business registration records, EIN filings, or officer information
Any one of these signals warrants immediate investigation. Multiple signals at once likely means an active compromise.
What is the business impact of digital identity theft?
The financial damage is severe and well-documented. PwC's Global Economic Crime and Fraud Survey found that one in five large companies, those with global revenues exceeding $10 billion, reported a fraud incident with a financial impact of more than $50 million.
The blast radius extends well beyond the balance sheet. Business identity theft also disrupts cash flow, damages creditor and supplier relationships, and creates lasting reputational harm. Recovery often takes months, and some relationships never fully recover.
Digital identity theft leads to these outcomes at scale:
- Asset misappropriation
- Unauthorized trading
- Intellectual property (IP) theft
- Money laundering
- Tax fraud
What types of digital identity fraud target businesses?
Attackers do not pick a single method. They cycle through tactics until something works. These are the fraud types most likely to hit your business.
Financial identity theft: A bad actor obtains your EIN, bank account information, or credit profile to open fraudulent lines of credit, file fake UCC liens, or gain access to financial systems. This targets the business entity directly.
Tax identity theft: False tax returns are filed under your business's EIN to claim and collect refunds before you do.
Identity cloning: A cybercriminal obtains business registration details or personal information to impersonate your company and conceal their own identity.
Synthetic identity theft: A bad actor creates a new identity using real and fabricated details, such as an actual EIN combined with fictional officer information, to evade anti-fraud systems. Synthetic fraud now accounts for 10 to 15% of charge-offs in unsecured lending portfolios, according to McKinsey.
Social media identity theft: A form of identity cloning in which a social media account for an individual or brand is imitated to defraud online contacts.
Website defacement: Criminals manipulate or hijack your web presence to damage your brand, spread misinformation, or redirect customers to malicious sites.
Trademark ransom: A fraudster registers your business name or logo as an official trademark and demands payment to release it back to you.
How digital identity fraud happens: 11 common attack tactics
Attackers do not limit themselves to a single approach. Understanding each tactic is the first step to closing the gaps in your defenses.
- Phishing: Fraudulent messages designed to trick a victim into divulging sensitive information.
- Credential stuffing: Collections of usernames and passwords from data breaches, used to access accounts across other platforms.
- Malware attacks: Unauthorized, malicious software deployed onto a business system.
- Malicious links: URLs distributed through spam or phishing campaigns to deploy malware.
- Keystroke recording (keylogging): Captures keys struck on a keyboard to steal passwords and sensitive information.
- Spyware: Malicious software that gathers sensitive information and transmits it to a third party.
- Open-source intelligence (OSINT): Collection of information from publicly available sources to build a profile on a target organization.
- SIM jacking: Exploiting two-factor verification processes or bribing a carrier employee to gain control of a victim's phone number.
- Pretexting: A cybercriminal fabricates a scenario to extract account details, often impersonating someone in authority.
- Email hijacking: Gaining access to an email account via malicious login pages or keylogging, then using that access to intercept communications or initiate fraudulent transactions.
- Fake social media connections: Created to access data, scrape sensitive information, or distribute malicious links.
What you can do:
- Audit access and authorization points across your organization. Identify dormant credentials, over-permissioned accounts, and unmonitored service logins, then close the gaps before attackers find them.
- Enforce strong, unique credential policies and mandate password manager adoption across your team, especially for accounts that touch customer data, financial transactions, or document workflows.
- Enable multi-factor authentication on all business accounts.
- Use liveness-detection identity verification at critical transaction touchpoints.
- Maintain cryptographic audit trails via platforms like Proof to deter and document fraud attempts.
- Conduct regular credential hygiene reviews and monitor business credit bureaus quarterly.
How AI and deepfakes are changing digital identity fraud
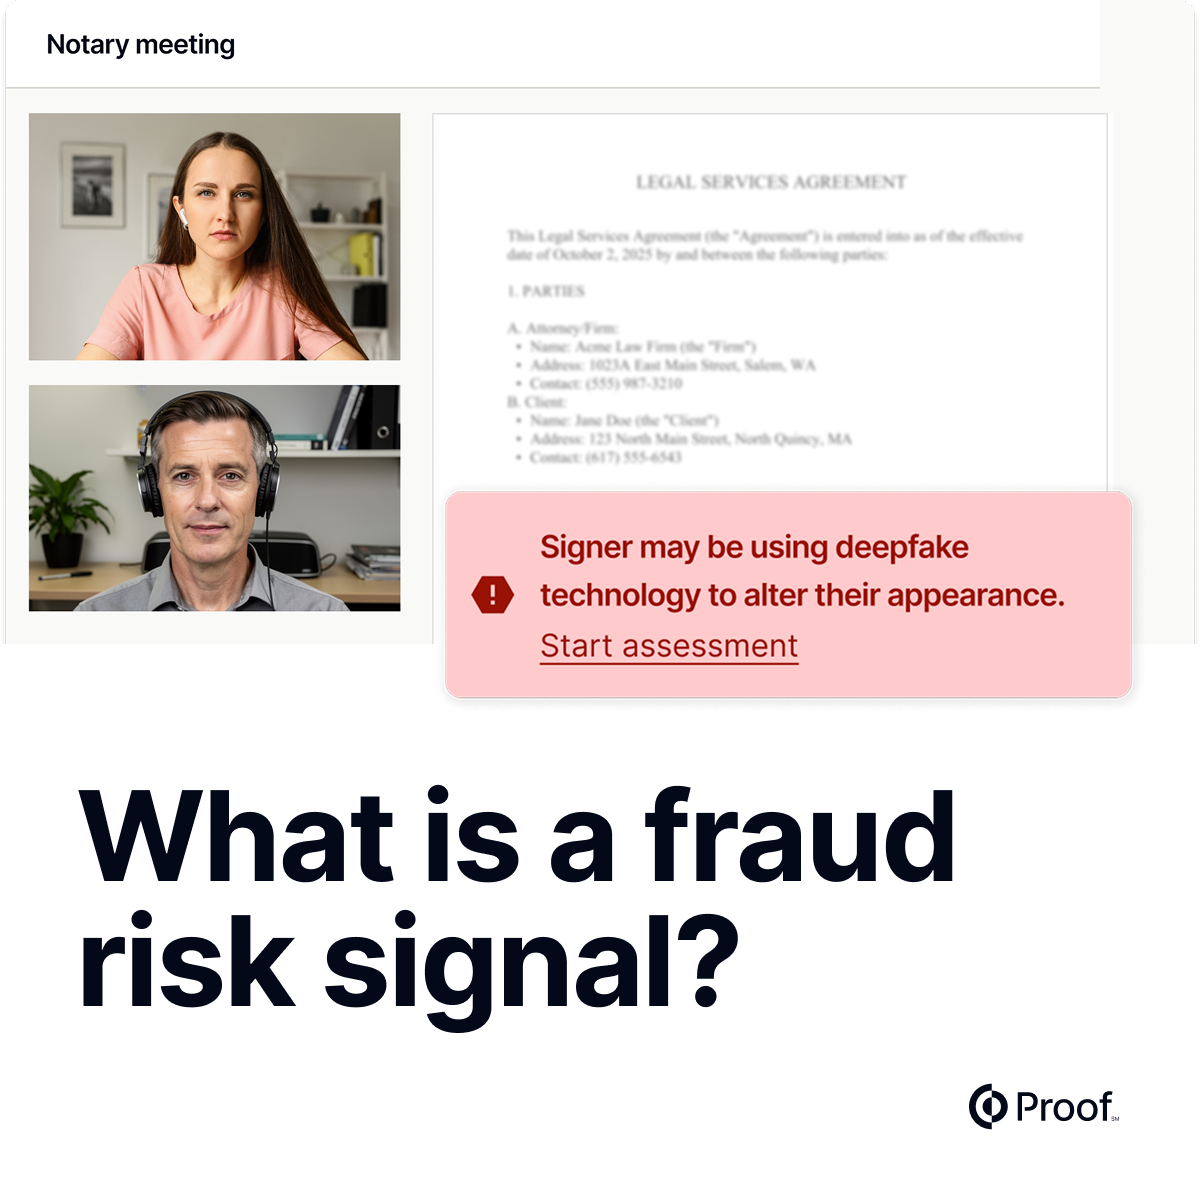
The threat landscape has shifted. Attackers now use AI-generated deepfakes to bypass biometric checks, fabricate video identities, and impersonate executives in real time. Automated systems that rely on appearance alone cannot reliably distinguish a live person from a convincing synthetic one.
This is where human-in-the-loop verification becomes critical. When automated identity checks fail or produce ambiguous results, escalating to a live agent who can conduct a recorded video review adds a layer of scrutiny that AI-generated fraud cannot easily defeat.
Synthetic identity fraud compounds this problem at scale. Fraudsters combine a real EIN or Social Security number with fabricated officer information, then gradually build a credit profile over months before executing a large-scale fraud event. By the time detection occurs, the damage is already done.
10 ways to protect your business from digital identity fraud
Businesses now have strong, layered tools available. Here are the most effective steps:
- Audit access and authorization points. Every active digital account is a potential entry point. Conduct regular access audits to identify dormant credentials, over-permissioned accounts, and unmonitored service logins across your organization's systems. Close the gaps before attackers find them.
- Enforce strong credential policies across your organization. Weak or reused passwords are an open invitation. Require strong, unique credentials for every business system and mandate password manager adoption across your team, especially for accounts that touch customer data, financial transactions, or document workflows. Tools like LastPass, Dashlane, or Keeper make this straightforward to deploy at scale.
- Use multi-factor authentication. Setting up multi-factor authentication on your most sensitive accounts adds a critical layer of security to your login process. Even if a password is stolen, MFA makes it significantly harder for a cybercriminal to access your account.
- Switch to online notarization. Businesses can deter fraud in notarizations by adopting an online notarization process. Proof uses multiple types of verification that go well beyond the traditional notarization process, including government ID scanning, biometric matching, and liveness detection.
- Monitor bank statements. Keeping a consistent eye on account activity helps you spot irregularities and fraudulent transactions before they compound. Set up transaction alerts at your bank to flag activity above defined thresholds.
- Monitor business credit and guard your EIN. Unlike personal credit, there is no centralized alert system for business credit. Regularly checking your company's credit report through business credit bureaus such as Dun & Bradstreet, Equifax Business, and Experian Business can surface unauthorized lines of credit or other anomalies before they do serious damage. Treat your EIN the same way you would treat a Social Security number. If you discover unauthorized filings, contact the IRS immediately via Form 14039-B to report business identity theft. The faster you act, the smaller the blast radius.
- Adjust privacy settings on business social media accounts. Use privacy settings to safeguard business information and limit what attackers can use against you. Regulate visibility on all official accounts and restrict access to posting privileges.
- Only download apps from official app stores. Outside Google and Apple app stores, many third-party providers do not conduct testing for potential malware. The risk of third-party downloads is real and entirely avoidable.
- Establish a cyber recovery plan tied to your identity infrastructure. When a breach occurs, you need more than a backup. Map out how your team will verify the identity of anyone requesting access to restored systems, so recovery does not become another attack vector.
- Keep your devices and software updated. Treat software updates as a fraud control. Unpatched vulnerabilities are a primary entry point for credential theft and malware. Enforce update policies at the organizational level, including for any tools that touch identity verification or document workflows.
How Proof helps protect businesses from digital identity fraud
Fraud strikes at every point where identity, documents, and authorization intersect. Proof gives businesses a layered defense across the full customer lifecycle:
- Defend: AI-driven fraud intelligence that monitors cross-channel activity, detects deepfakes, and routes risk in real time
- Identify and Verify: Identity verification with biometric matching and human-in-the-loop review for high-risk interactions
- Sign and Notarize: Identity-backed signatures and notarizations with a tamper-evident audit trail
- Certify: Cryptographically signed, verifiable records for documents, data, and transactions, each bound to a verified legal identity
Every interaction on Proof's platform produces an audit trail tied to a verified identity. When the risk is high, the identity evidence needs to be unimpeachable.
See how Proof Defend protects your transactions from digital identity fraud.